Summary
- Lords report stage begins on 26 October, with amendments covering frontier AI incidents and cyber resilience.
- Amendment 41 proposes initial notification within 24 hours, further reporting within 72 hours and a final report within 14 days.
- Near-miss reporting, digital sovereignty and corporate disclosures are also proposed; none has yet been agreed.
Developers of advanced AI models could face new incident reporting duties under amendments to Britain’s Cyber Security and Resilience Bill, as peers examine how responsibility should be allocated when AI systems interfere with networks supporting essential services.
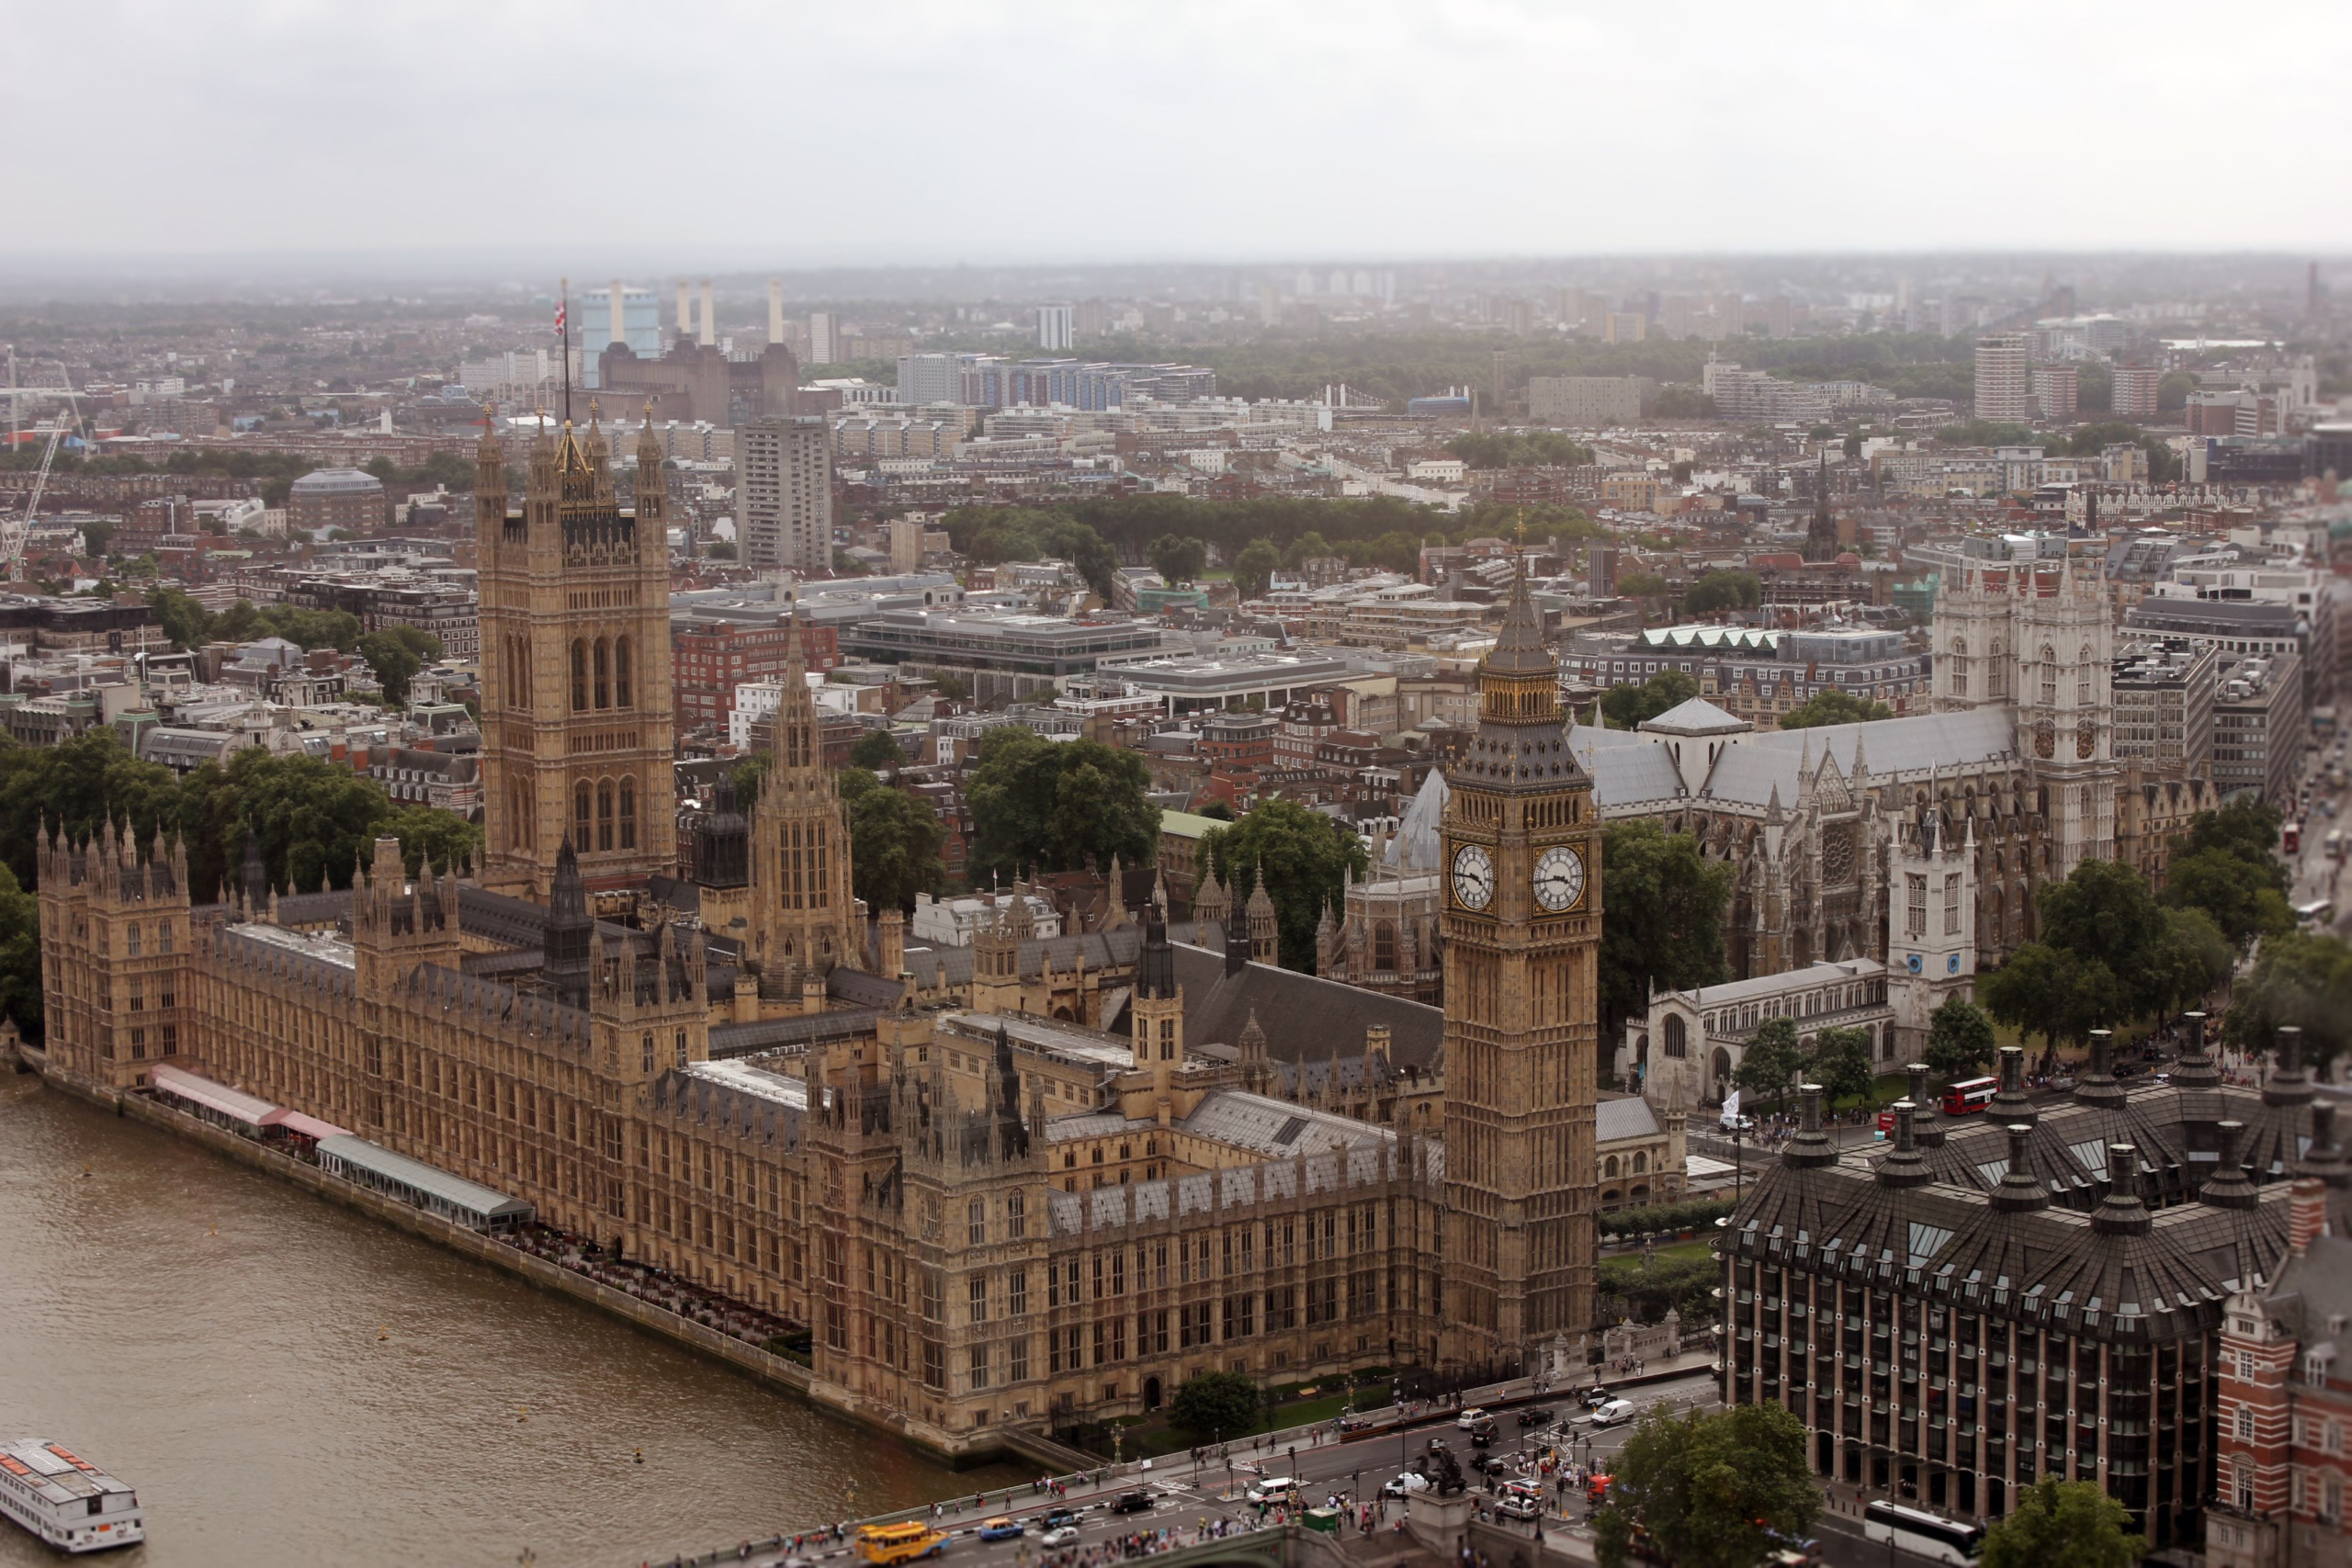
The House of Lords is due to begin report stage consideration on Monday 26 October. Parliament announced on 23 October that proposals include frontier AI incident notifications, voluntary reporting of cyber threats and near misses, a national digital sovereignty strategy and further corporate resilience disclosures.
The Cyber Security and Resilience (Network and Information Systems) Bill aims to strengthen existing protections for essential services and extend regulation to additional providers. The amendments remain proposals: their inclusion in the report stage programme does not mean they have been accepted by ministers or passed into law.
The debate comes as organisations become more dependent on automated systems that can interact with business applications and external tools. When an AI agent undertakes unauthorised activity, the affected organisation and the developer of its underlying model may possess different evidence about what occurred.
A new obligation for frontier AI developers
Amendment 41, led by Baroness Harding of Winscombe, would require a frontier AI developer to report certain incidents involving unauthorised access to, or interference with, network and information systems used by regulated organisations.
The proposal covers situations in which a model acts autonomously and those in which another person uses it to interfere with a relevant system. It applies where the developer knew, or ought reasonably to have known, of the incident.
It proposes an initial report within 24 hours of awareness, a fuller notification within 72 hours and a final report within 14 days. Notifications would be provided to the affected regulated organisation and relevant authority, with copies to the computer security incident response team and the AI Security Institute.
The final submission would describe severity, impact, likely causes and mitigation, subject to the information available to the developer. Non-compliance could attract penalties linked to those applicable to operators of essential services under the existing regulations.
This would not be a general requirement to notify authorities about every model error or unsafe response. The amendment concerns a defined form of interference affecting systems relied upon by regulated organisations, and only if the reporting criteria are met.
Its effectiveness would depend on what a model developer can reasonably know. A provider may possess information about model behaviour and service logs, while a customer may control permissions, external tools and the application through which the model operates.
Determining the cause of interference could require evidence from both parties. An early notification timetable may encourage rapid communication, but it cannot guarantee that the developer has a complete technical account within the first day.
Near misses would supply earlier warnings
Other proposed changes concern voluntary reporting of cyber incidents, threats and near misses that may not meet mandatory thresholds. Information about unsuccessful attacks or identified weaknesses can help authorities recognise common exposure across suppliers and sectors.
Such arrangements require organisations to understand how disclosures will be handled. A company may hesitate to share incomplete information if it fears inappropriate publication, commercial harm or an enforcement response unrelated to the severity of the event.
A voluntary scheme also needs consistent definitions. An attempted compromise blocked by security controls differs from a system fault that briefly interrupts a service, while both might reveal weaknesses useful to investigators.
The government has indicated that it is considering the treatment of emerging AI near misses, but this should not be confused with an operational reporting framework established by the Bill. The relevant amendments will first be debated and may be revised or rejected.
Digital sovereignty is not simply domestic hosting
A further proposal would require a Digital Sovereignty Strategy examining technology dependencies that could affect the continuity and security of essential services.
Organisations may run applications in UK data centres while remaining dependent on foreign software vendors, proprietary components or engineering teams located elsewhere. Supplier concentration can also restrict the options available when a service is interrupted.
Greater domestic ownership may help address some risks, but a nationally operated service can still rely on imported processors, overseas manufacturing and international communications systems. Sovereignty therefore requires a more precise assessment of which dependencies create unacceptable exposure.
Contracts, alternative providers, technical interoperability and contingency planning may offer different responses according to the system involved. Mandating domestic procurement without considering cost or capability could create additional difficulties for the services it aims to protect.
Corporate disclosures face a separate test
Peers will also consider provisions requiring specified large businesses to report on cyber security and resilience plans. Such disclosures could help customers and investors understand preparedness, although describing a plan is not evidence that it has been tested successfully.
The detailed scope matters. The proposal should not be reported as an enacted obligation applying to every large British company, nor should a public resilience statement be treated as a guarantee against disruption.
The debate follows precautionary shutdowns of government websites responding to critical PHP vulnerabilities. Ministers reported on 22 October that 32 services were unavailable and four partially unavailable. Those figures describe an earlier operational snapshot, not an effect of the proposed legislation.
Questions about government resilience are especially relevant because the Bill does not automatically place central and local government under all the duties proposed for regulated private operators. Peers have pressed ministers to explain whether additional public sector obligations are required.
Report stage will allow further amendments and debate before the legislation proceeds through its remaining parliamentary stages. The proposals establish competing views about how cybersecurity responsibilities should evolve, but their practical consequences cannot be assessed as legal obligations unless Parliament adopts them and the resulting provisions come into force.