

Summary
- The European Cybersecurity Competence Centre's Governing Board amended its 2025–2027 Digital Europe Cybersecurity Work Programme during meetings in Cyprus.
- The amendment adds a section dedicated to implementing the EU's July 2026 Action Plan on Cybersecurity and Artificial Intelligence.
- The October announcement does not identify a new funding allocation, grant award or completed AI cybersecurity deployment.
The European Cybersecurity Competence Centre has amended its multi-year cybersecurity work programme to include implementation of the European Union’s action plan on artificial intelligence and cybersecurity, giving the policy initiative a defined place within the funding and capability framework managed by the Centre.
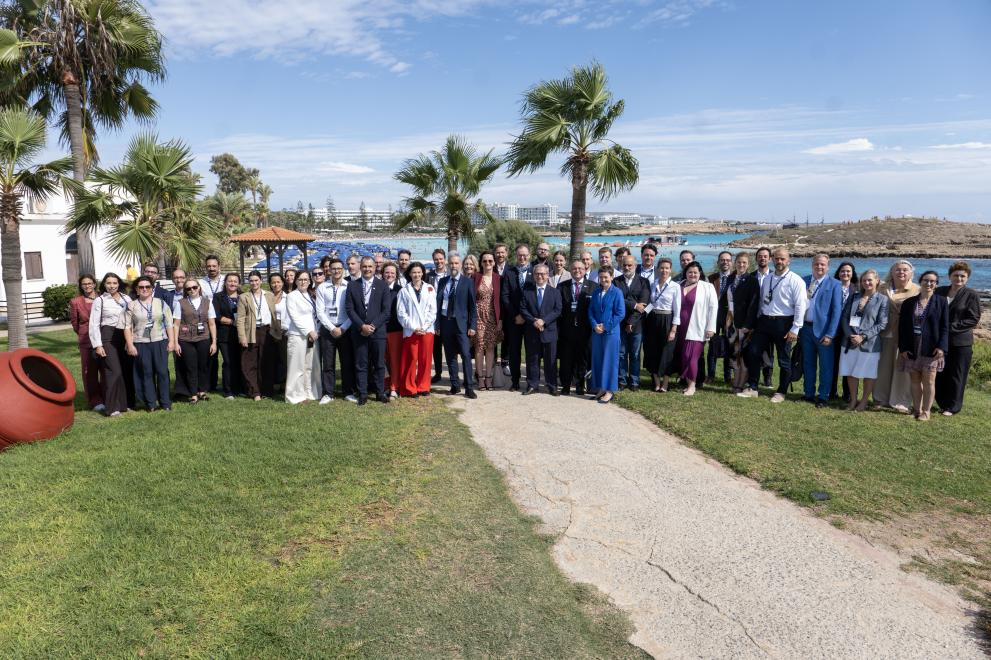
The decision was made by the Centre’s Governing Board during meetings in Cyprus on 13–15 October and announced on 16 October. It adds a dedicated section to the Digital Europe Cybersecurity Work Programme for 2025–2027, following the European Commission’s publication of its AI cybersecurity action plan in July.
The Centre, known as the ECCC, coordinates European cybersecurity capability development and manages relevant funding activities under the Digital Europe Programme. Its work connects EU institutions, national authorities, researchers and technology businesses seeking to strengthen cyber resilience and develop specialised expertise.
Although the amendment establishes a programme priority, the October announcement does not identify a new funding allocation, procurement award or completed project. Its immediate significance is the formal inclusion of AI cybersecurity implementation within an existing programme, rather than the deployment of a new European security system.
AI changes both attack and defence
The European Commission’s Action Plan on Cybersecurity and Artificial Intelligence was published on 7 July 2026. It describes how advanced AI can support defensive activities while also enabling malicious actors to identify weaknesses, automate parts of attacks and increase the speed of cyber operations.
Security teams already use software to monitor systems, detect unusual activity and investigate incidents. More capable AI could assist with examining large quantities of information and selecting defensive actions, although its usefulness will depend on the accuracy of its outputs and the authority granted to it.
Similar capabilities can be exploited by attackers. Tools that help defenders examine software for vulnerabilities may also help hostile actors search for weaknesses, while automation can reduce the time required to repeat certain malicious activities.
The EU’s action plan therefore addresses both the security of systems using AI and the possibility of applying AI to improve cybersecurity. These are related but different tasks: protecting an AI system against manipulation does not automatically provide the capabilities needed to defend an organisation’s wider infrastructure.
The Commission’s July plan proposes work on AI evaluation, guidance for organisations, the use of AI in cyber defence and the development of European capabilities. The ECCC’s October decision links that existing policy agenda to a programme responsible for supporting cybersecurity technology and expertise.
However, the Board’s announcement does not explain how every part of the action plan will be translated into individual funding calls, technical requirements or delivery milestones. Those details will need to be assessed in subsequent implementation documents.
National centres connect funding with industry
The Cyprus meetings also brought together representatives from the EU’s National Coordination Centres, which connect national cybersecurity communities with European initiatives.
These organisations help businesses, researchers, public authorities and other participants identify relevant programmes and opportunities to develop cybersecurity capabilities. Their role is particularly important where expertise or infrastructure is distributed between countries and individual organisations cannot justify building every specialist resource independently.
During the meetings, representatives exchanged information about existing activities and national cybersecurity ecosystems, while discussing ways to improve cooperation across the network. Presentations from Digital Europe projects provided examples of work already supported under European cybersecurity initiatives.
Greater cooperation can help avoid duplicated development effort, but shared capabilities also depend on common technical arrangements and clear responsibilities. Cybersecurity tools may need access to sensitive information, making security controls and lawful data processing important conditions for their use.
For smaller European technology suppliers, cooperation can provide access to partners and programmes that would otherwise be difficult to reach. Whether the latest AI amendment generates additional commercial opportunities depends on later decisions about eligibility, procurement and available funds.
The ECCC also reported progress on governance arrangements and its working groups. Its Governing Board approved a proposed membership list for a Strategic Advisory Group intended to provide independent expertise and advice.
That approval does not establish that the advisory group has already completed work or issued recommendations. The Centre describes its establishment as forthcoming.
Existing funds cannot be counted twice
The ECCC already operates within a substantial European cybersecurity funding programme. In September 2026, it announced a separate Digital Europe call providing up to €96 million for cybersecurity capabilities and related development activities.
That earlier call predates the October decision and must not be presented as funding newly allocated under the AI action plan amendment.
Similarly, the work programme underwent previous amendments, including one adopted in July 2026. The latest announcement confirms a further change in direction, but the programme’s earlier funding arrangements and activities remain separate from the new section unless the Centre identifies a specific connection.
European cybersecurity activities also operate alongside existing legislation, including the NIS2 Directive, the Cyber Resilience Act and the Cyber Solidarity Act. The AI cybersecurity action plan builds on this wider policy framework rather than replacing the legal requirements attached to individual sectors or products.
A work programme amendment does not itself require businesses to adopt a particular security product or establish a new compliance deadline. Such obligations would need to arise from the relevant legal instruments rather than the funding programme alone.
These distinctions are commercially important because technology companies may monitor European policy announcements for funding opportunities or emerging requirements. An adopted programme priority can signal future activity, but it is not equivalent to a contract, grant decision or binding technical standard.
Implementation remains the next step
AI cybersecurity has become a more explicit part of the EU’s programme architecture at a time when institutions are examining how to govern advanced models and counter their misuse.
The ECCC’s decision gives the Centre an implementation role within the Digital Europe Cybersecurity Work Programme, supported by its existing relationships with national coordination bodies and the broader European cybersecurity community.
The public announcement leaves several operational matters unresolved, including which projects will be supported, whether existing funding lines will be revised and how the effectiveness of new activities will be assessed.
Those details will determine whether the programme amendment results in new technology development, additional shared capabilities or changes to initiatives already under way. The confirmed October milestone is the amendment itself, with specific awards and delivery outcomes still to be established.


