Summary
- DSIT research finds 35% of UK adults provided informal digital support to another person during the previous year.
- Proxy help is common for public services, health appointments, bills, and applications, sometimes involving supporters using another person’s login credentials.
- Researchers recommend designing supported access into services, improving formal delegation, expanding community support, and creating cross-sector inclusion standards.
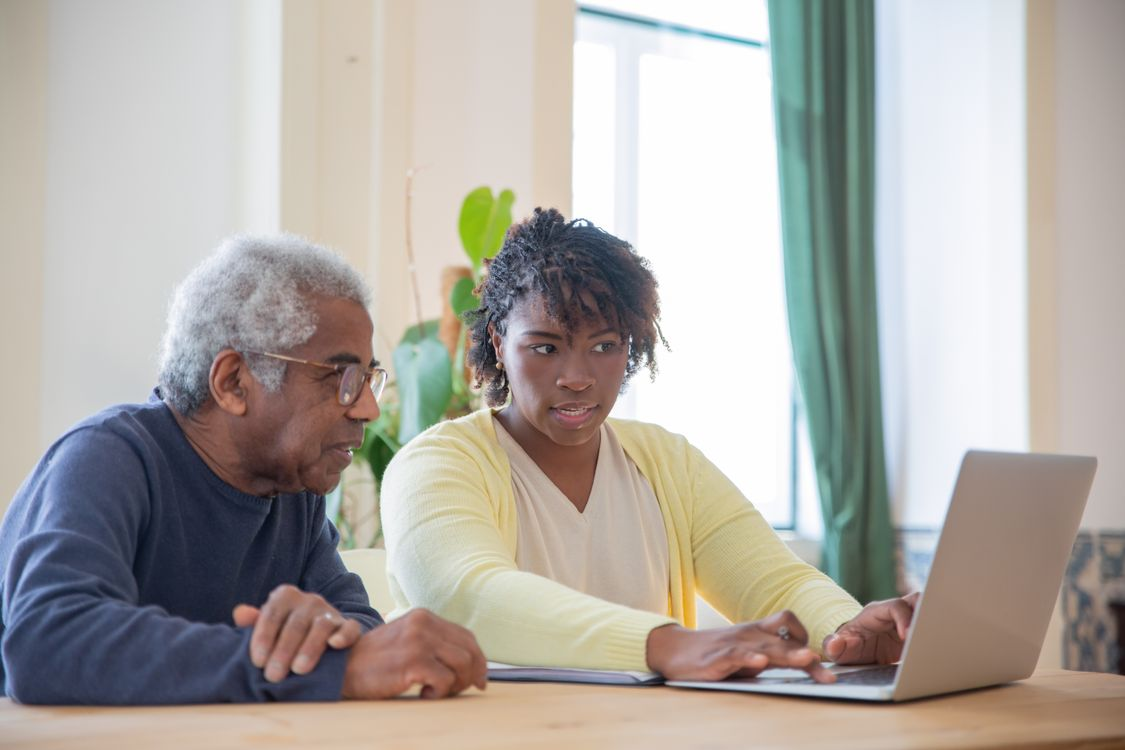
The Department for Science, Innovation and Technology has put numbers around an unofficial layer of Britain’s digital economy: relatives, friends, neighbours, and colleagues routinely acting as unpaid support staff for people who cannot comfortably navigate online services alone.
Research commissioned by the department found that 35% of UK adults had provided informal digital support during the previous year, helping another person use online services or technology outside a formal paid or volunteering role. For many people receiving that help, the supporter is their principal — and sometimes only — route into an increasingly digital system.
The study distinguishes between teaching someone to use a service, advising them while they complete a task, and proxy support, where the helper performs the online task on the other person’s behalf. That final category is particularly important because it often appears when the task is urgent, infrequent, complicated, or financially consequential.
Researchers found proxy support was used by 55% of supporters helping someone interact with public services, while half of those helping with health appointments used the same approach. Paying bills and completing applications also frequently involved one person taking over another person’s digital task rather than teaching them to complete it independently.
Services are often designed for one user
That pattern exposes a mismatch between the way many digital services are designed and the way they are used in practice. Authentication systems generally assume that one account belongs to one person using their own credentials, yet people who struggle with digital services regularly rely on somebody they trust to act alongside or on behalf of them.
Where a service does not provide a clear delegation mechanism, households invent one. The research found that almost a third of supporters had used somebody else’s login details to manage online banking or financial accounts, while only 7% had been formally added to the relevant account as a third party.
Healthcare shows a similar gap. Twenty-six per cent had used another person’s login details to manage healthcare online, compared with 8% who had been formally added to someone else’s NHS App.
Those workarounds can solve an immediate problem while weakening the security model around the service. Password sharing makes it harder to know who carried out an action, while unrestricted account access may give a helper substantially more authority than the supported person intended. It can also create difficulty when the relationship changes or access needs to be withdrawn.
The study consequently recommends making formal proxy support a normal service-design pattern rather than an exceptional process hidden behind administrative complexity. Researchers discuss more granular, time-limited permissions that allow another person to perform specific actions while leaving the account owner in control.
Security and inclusion collide at authentication
Identity verification is one of the difficult points because stronger authentication can protect accounts while simultaneously making supported access harder. Two-factor authentication, device controls, and identity checks work well when the person using the service can complete every step independently; they become more complicated when another person is legitimately helping.
The researchers argue that proxy access should therefore be considered across the entire service journey rather than bolted onto the end. That could include explicit supporter identities, visible delegated permissions, transaction monitoring, reversible access, and offline alternatives where a digital route remains unsuitable.
The findings also complicate the assumption that digital inclusion can be solved primarily by teaching more skills. Some people in the study wanted to become more independent, while others faced barriers that made continuing assistance appropriate. Older people, disabled users, people with limited confidence, and those confronting high-stakes or unfamiliar tasks may need different kinds of support at different moments.
Teaching was associated with greater reported independence, although the report explicitly warns against reading that relationship as straightforward causation. People who are more motivated or better positioned to learn may be more likely to receive teaching support in the first place.
Proxy assistance can likewise create dependency if somebody routinely takes over every difficult task, but removing that help without providing a workable alternative can exclude the person entirely. The service-design challenge is therefore to allow assistance without making another individual a permanent single point of failure.
The study sits inside the government’s wider Digital Inclusion Action Plan. A progress report published in March said 1.6 million people remained without an internet connection, while the programme covers connectivity, devices, skills, accessible digital services, and local support. Government guidance also says public services should retain supported offline routes where needed rather than making digital the sole option.
The new research shifts part of that debate towards the services themselves. If a third of adults are already helping somebody else operate online, the support system is not marginal behaviour confined to a small digitally excluded population; it is an informal operating layer beneath banking, healthcare, government, shopping, communications, and other services.
Organisations can either continue treating those helpers as anomalous users or design for the reality that legitimate assistance occurs. The former approach leaves families sharing passwords and negotiating authentication systems built to keep them out, while the latter requires product teams to think carefully about consent, identity, security, accountability, and revocation.